 In Mountain View.
Monday, April 16, 2007

AOL OpenAuth Launches!
Praveen just blogged about
the launch of AOL's Open
Authentication service. We'll be talking about this and more at
Web 2.0 Expo. Why launch another authentication service when we
already support OpenID? Because there are lots of cool things that
OpenID doesn't yet support. I think that it really supports
user-controlled consent and permissions, for example. And Praveen is
already working within the OpenID community to add some of these
capabilities as well.
Sunday, April 15, 2007
Bee Colony Collapse Disorder and Cell Phones
This
story is popping up all over, apparently due to the possible
correlation with cell phone use. It's funny that "four years left
before we all starve to death" doesn't get big headlines, but "cell
phones might cause bee colonies to collapse" does... The graduate optimization
class that my wife TAs at Stanford just finished their class
project. It was to write code to optimize food production given that
you need to allocate some land for natural bee colonies. Apparently a
lot of the commercial bee colonies get trucked around to do their jobs
from field to field, and bee colony collapse has been causing a lot of
problems with this system. Whatever the cause, decentralization of bee
production seems like a good idea.
Friday, April 13, 2007
Talk @ Web 2.0 Expo: Mashing Up with User-Centric Identity
Praveen and I are going to tag-team in Mashing Up with User-Centric Identity, at Web 2.0 Expo. It's about how to leverage user centric identity to combine services in a seamless way:
Date: Wednesday, April 18
Time: 1:00pm - 1:50pm
Location: Room 2014, Web 2.0 Expo, San Francisco CA
In a Web 2.0 world, users combine services from many providers. Having a common identity across providers eliminates a barrier to entry and adopting a user-centric identity system puts the user in control of how their information is combined. This session is about the opportunities and issues involved specifically with adopting open protocols, the solutions they provide, and open issues that remain to be solved. These include user experience, permission management, and mashup API authentication.Unfortunately this conflicts with David Recordon's Implementing OpenID talk at the same time, which is likely to be really good and draw a similar crowd. (Could we simulcast?)
Date: Wednesday, April 18
Time: 1:00pm - 1:50pm
Location: Room 2014, Web 2.0 Expo, San Francisco CA
Thursday, April 12, 2007
Animated Bayeux Tapestry by The People Formerly Known as the Audience
Very cool video created by David Newton of the SCA group on MySpace, highlighted by the moderator, and being emailed around today. I plan to put this up on a loop in our break room.
Sunday, April 1, 2007
Announcing 10100100101.com
I'm excited to announce that AOL has decided to leapfrog the competition
and come out with the next generation blogging service, even more
streamlined than Twitter. It's blogging pared down to its bare
essentials. And it works great on mobile devices, RSS, and Atom feeds.
Here's how it works: You register your phone, and every 15 minutes, you get an SMS asking "How's it going? (0/1)". You send back 0 if you're feeling down, 1 if you're feeling good, and nothing if you're asleep. We call each of these a How's It Goin', or HIG. You can subscribe to your friends' HIGstreams and see how they're doing. And we're planning a visualization tool which maps the Buddy List connection matrix to a two dimensional projection showing how the emotional states of each buddy affects their neighbors:
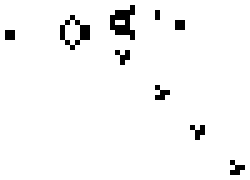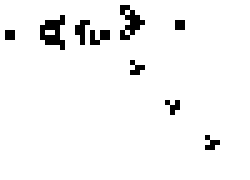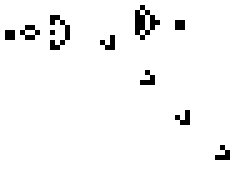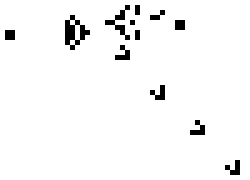
Interestingly, having either too few or too many happy buddies makes a buddy sad. Further research is needed.
Here's how it works: You register your phone, and every 15 minutes, you get an SMS asking "How's it going? (0/1)". You send back 0 if you're feeling down, 1 if you're feeling good, and nothing if you're asleep. We call each of these a How's It Goin', or HIG. You can subscribe to your friends' HIGstreams and see how they're doing. And we're planning a visualization tool which maps the Buddy List connection matrix to a two dimensional projection showing how the emotional states of each buddy affects their neighbors:

Interestingly, having either too few or too many happy buddies makes a buddy sad. Further research is needed.
Authenticated RSS Feeds: Drosophilia of Delegation?
Jon Udell has noticed that authenticated
RSS feeds don't work very well. It's a chicken and egg situation:
There are few authenticated RSS/Atom feeds because there are few feed
readers that deal with them, and vice versa. But beyond that
bootstrapping problem there's a larger one.
A lot of popular feed reader services such as My Yahoo or Bloglines are host based. With current feed authentication mechanisms, this means that you have to hand your user name(s) and password(s) to your feed reader service and let it impersonate you to do anything useful. Not great. Recently, Kim Cameron has been blazing away at the concept of impersonation, not just the problem of handing your password out. I'd like to suggest that authenticated feeds provide an ideal place to experiment with better approaches: They're read only, the bar is currently very low, and there's a whole host of immediate possibilities that would become possible once you can cleanly authorize a feed reader to read feeds on your behalf. I think the right way to do this is through a lightweight assertion mechanism that lets you say "I authorize service X to asynchronously read feed Y on my (Z's) behalf".
I'm still trying to digest all of the twists and turns of the thread below. I am pretty sure that whatever solution is adopted, it has to cleanly allow for the "allow a service to read a feed" to be at all useful.
The Impersonation/Delegation Discussion
Presented in backwards chronological order
Dramatis Personae: Eve Mahler, Kim Cameron, Conor Cahill, Pete Rowley, Phil Windley
Phil Windley: On Impersonation and Delegation
Conor Cahill: Delegation, Impersonation, and downright access
Pete Rowley: The umpire delegates back
Conor Cahill: SAML, Liberty, and user presence
Kim Cameron: Drilling further into delegation
Kim Cameron: Wrong-headed impersonation
Tags: authentication, delegation, openid, cardspace, feeds, impersonation, drosophili
A lot of popular feed reader services such as My Yahoo or Bloglines are host based. With current feed authentication mechanisms, this means that you have to hand your user name(s) and password(s) to your feed reader service and let it impersonate you to do anything useful. Not great. Recently, Kim Cameron has been blazing away at the concept of impersonation, not just the problem of handing your password out. I'd like to suggest that authenticated feeds provide an ideal place to experiment with better approaches: They're read only, the bar is currently very low, and there's a whole host of immediate possibilities that would become possible once you can cleanly authorize a feed reader to read feeds on your behalf. I think the right way to do this is through a lightweight assertion mechanism that lets you say "I authorize service X to asynchronously read feed Y on my (Z's) behalf".
I'm still trying to digest all of the twists and turns of the thread below. I am pretty sure that whatever solution is adopted, it has to cleanly allow for the "allow a service to read a feed" to be at all useful.
The Impersonation/Delegation Discussion
Presented in backwards chronological order
Dramatis Personae: Eve Mahler, Kim Cameron, Conor Cahill, Pete Rowley, Phil Windley
Phil Windley: On Impersonation and Delegation
Conor Cahill: Delegation, Impersonation, and downright access
Pete Rowley: The umpire delegates back
Conor Cahill: SAML, Liberty, and user presence
Kim Cameron: Drilling further into delegation
Kim Cameron: Wrong-headed impersonation
Tags: authentication, delegation, openid, cardspace, feeds, impersonation, drosophili
Subscribe to:
Posts (Atom)
